Web Application Attacks Explained: XSS, SQLi, CSRF & Session Hijacking
How Hackers Use Stored Cross Site Scripting (XSS) to Steal Session Cookies (and how to mitigate it)
XSS Attack Demo: How I Hijacked WordPress Admin Session Using Stored XSS
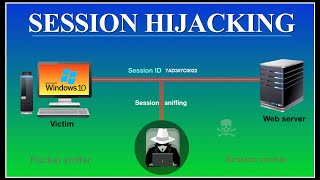
What is Session Hijacking and How it WORKS
How XSS Works — Reflected, Stored, DOM & Session Hijacking (Ethical Hacking)
Session Hijacking with Ettercap
Session Hijacking Attack | Session ID and Cookie Stealing | SideJacking
Deep Dive
Data is compiled from public records and verified media reports.
Last Updated: September 27, 2026
Conclusion
For 2026, Xss Session Hijacking remains one of the most talked-about information profiles. Check back for the latest updates.
Disclaimer: Disclaimer: All information is compiled from publicly available data, media reports, and analysis. Actual details may vary.
Summary
PentesterLab pentesterlab.com/ pentesterlab.com/exercises/xss_and_mysql_file KALI Linux kali.org/ ... Read the Cloud Threat Landscape Report → ibm.biz/BdabCs Learn more about the technology → ibm.biz/BdabCi ... In this video, I demonstrate how web This video covers part of the Web Application Attacks section of the CEH v11 blueprint, focusing on This video demonstration utilizes the Portswigger Web Academy (a free online training platform) to demonstrate how As a web developer transitioning into cybersecurity, I built a real-world Today in this video, you will learn what is For educational purposes only. Only test on systems you own or have explicit written permission to test.